Logins · about 10 minutes
Turn Off SSH Password Logins
What This Means
SSH accepts passwords, so every bot on the internet can keep guessing them.
Why It Matters
An SSH key can't be guessed. Once keys are the only way in, password-guessing attacks stop mattering.
Before you start
Do step 1 first and check your key works. If you turn passwords off without a working key, you lock yourself out.
- 1
Make sure your key works
On your own computer, create a key if you don't have one (ssh-keygen -t ed25519) and copy it to the server with ssh-copy-id root@your-server. Then check the server has it:
ls -l ~/.ssh/authorized_keys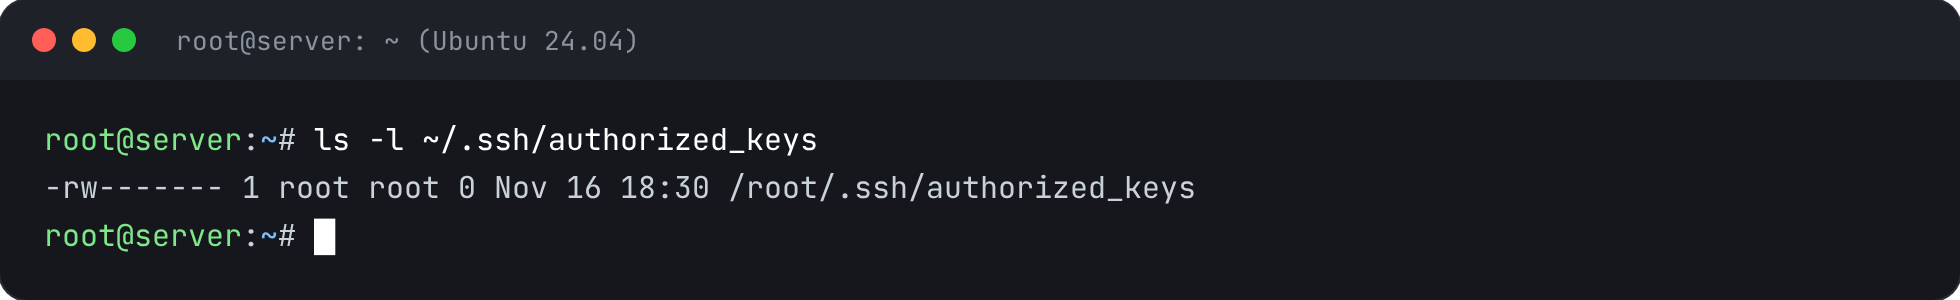
- 2
See the current setting
sshd -T | grep -iE '^(passwordauthentication|kbdinteractiveauthentication)'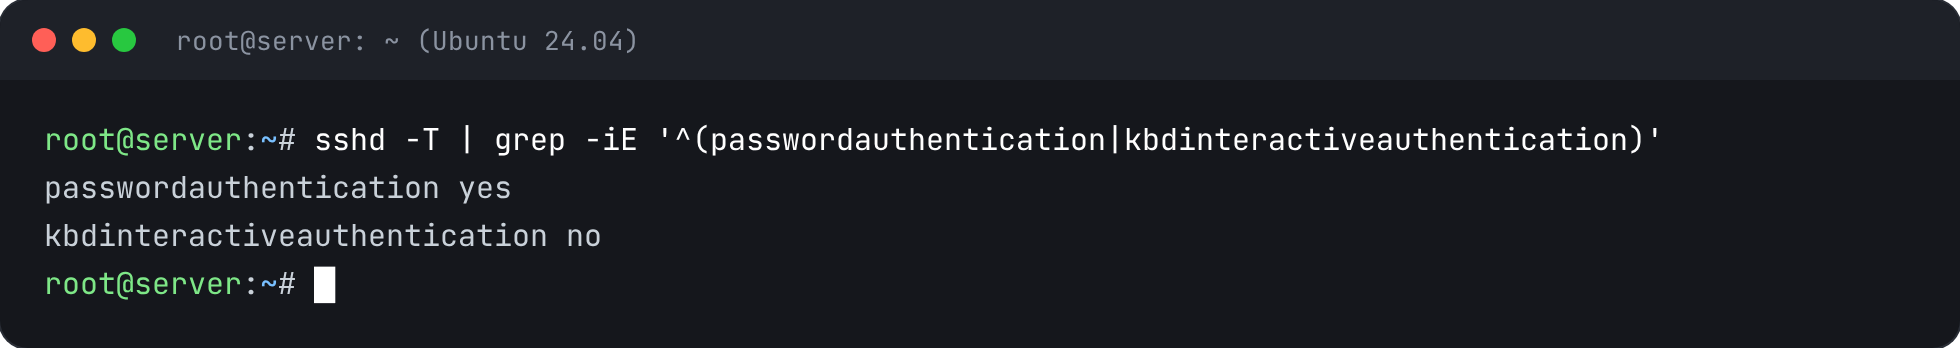
- 3
Turn passwords off
Settings in /etc/ssh/sshd_config.d/ are read first, and the first value SSH reads wins, so a file named 10-… beats the defaults and anything your host added (such as 50-cloud-init.conf).
printf 'PasswordAuthentication no\nKbdInteractiveAuthentication no\n' > /etc/ssh/sshd_config.d/10-frabs-keys-only.conf
- 4
Check and reload
sshd -t && systemctl reload ssh && echo reloaded
- 5
Confirm it worked
Both should now say no. Open a new window and log in with your key before closing the old one.
sshd -T | grep -iE '^(passwordauthentication|kbdinteractiveauthentication)'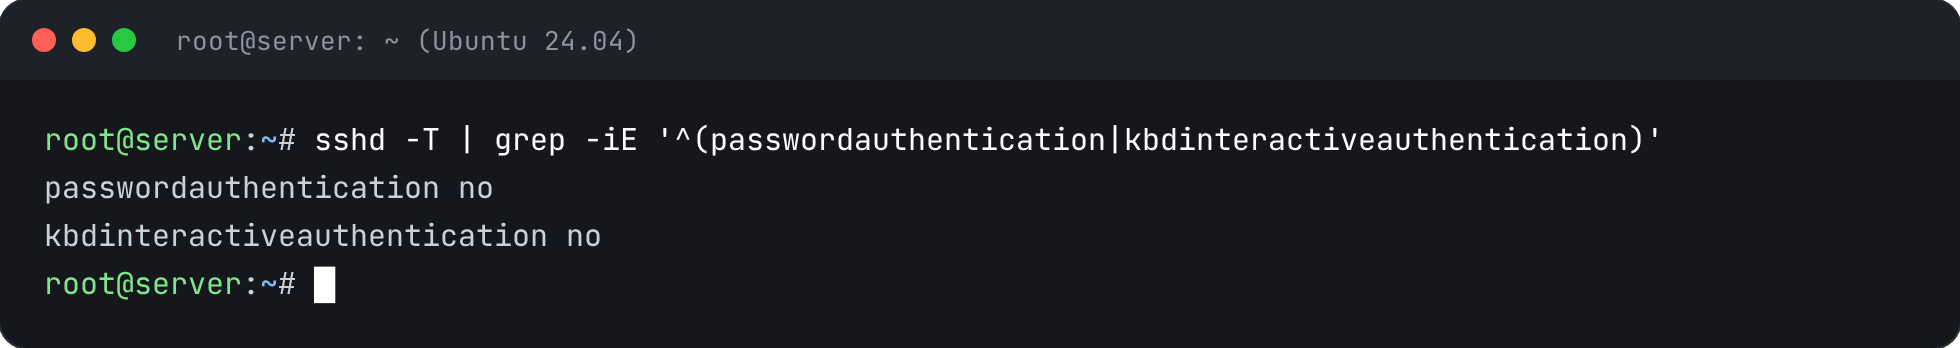


Check It’s Fixed
Run the security report again. This check should now pass.